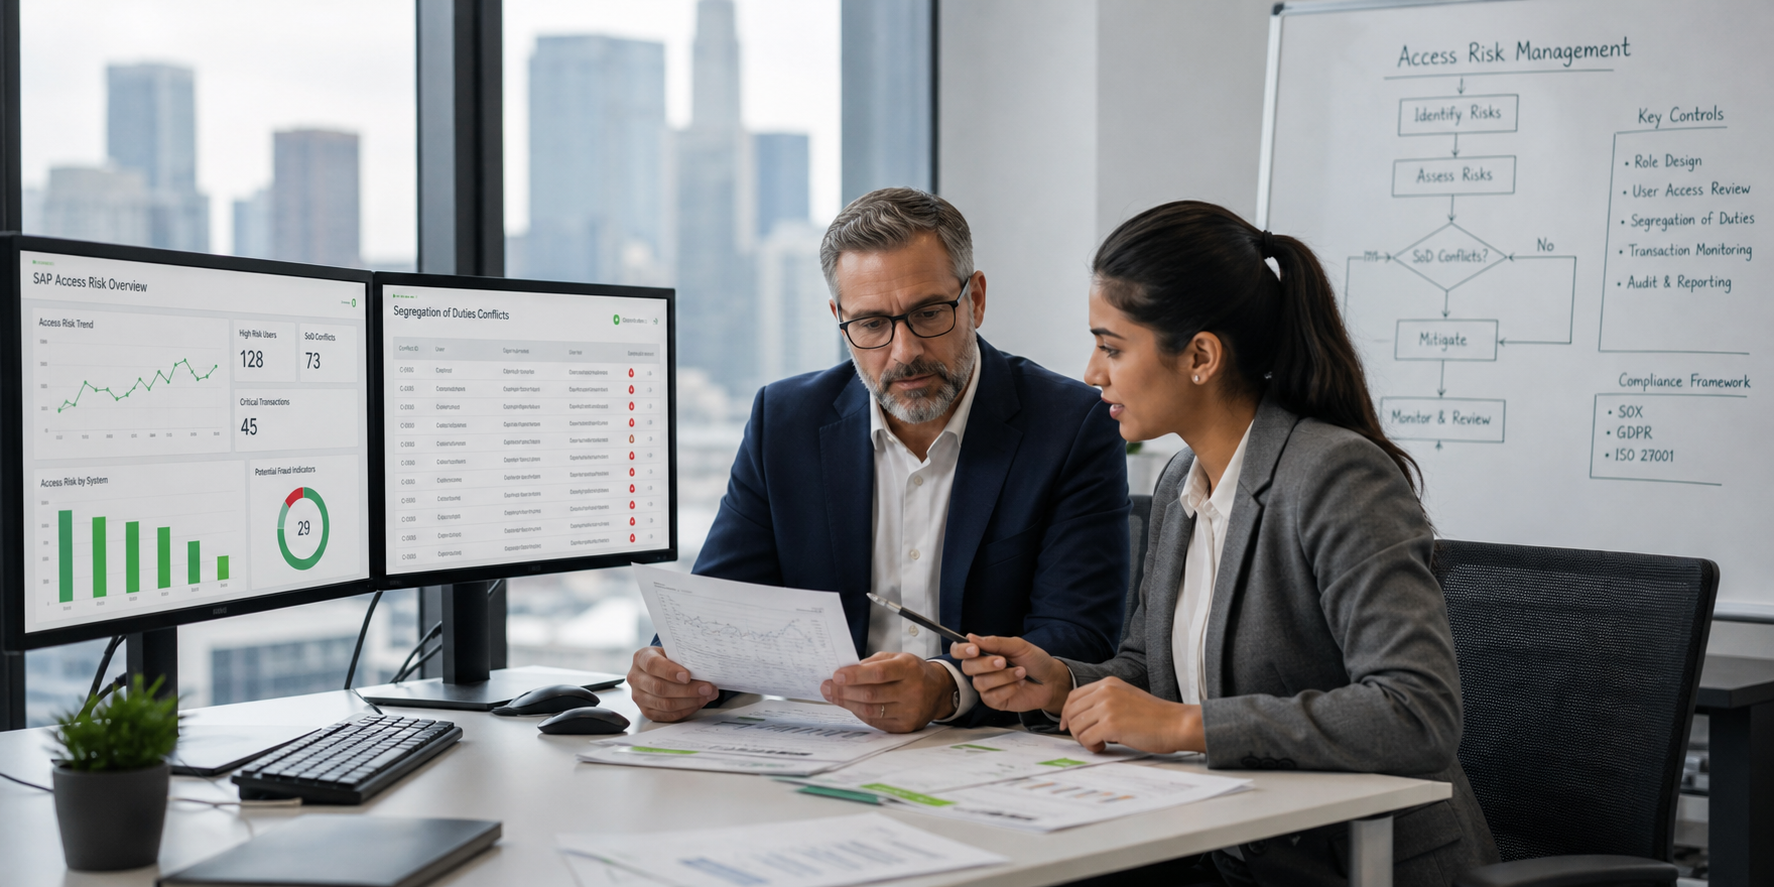
Most mid-market SAP teams know their segregation of duties (SoD) position needs attention. The difficulty is knowing where to begin when your team is small, your audit window is approaching and your current evidence sits across disconnected spreadsheets and role exports. Access risk management offers a structured path forward. Translating that concept into practical steps, though, requires a clear starting point.
This article outlines a repeatable process for identifying SoD risk priorities, assigning review ownership and building the kind of evidence trail that satisfies auditors. CERPASS helps mid-market teams structure this process with SAP BTP-based analysis and monitoring tools. The guidance is intended for mid-market SAP security, IT, compliance, risk and audit teams operating across Australia, New Zealand, Europe, the Middle East and Africa.
Key Takeaways: SAP Audit Readiness for Mid-Market Teams
- SoD conflicts in SAP user authorisations create measurable audit risk that manual checks struggle to detect consistently.
- A documented and versioned ruleset, not a spreadsheet, gives auditors the repeatable control evidence they expect.
- Assigning SoD risk ownership to business process owners keeps accountability clear and review cycles manageable.
- Delta-based user access reviews reduce reviewer fatigue and produce stronger evidence than full recertification campaigns.
- CERPASS supports SoD Analysis, user access reviews and dashboards that keep evidence BTP-based current between audits.
Why Do Manual SoD Checks Create Audit Risk?
Spreadsheet-based SoD checks typically rely on periodic exports of user-to-role assignments, compared against a static conflict matrix. The gap between each export creates a blind spot: if a user receives a new role that introduces a conflict, that exposure persists undetected until the next scheduled review.
Consider a practical example: a user who holds authorisations to both create a vendor master record and release a payment. That combination opens the door to fictitious vendor fraud. A quarterly spreadsheet review might surface it eventually, but the exposure may have persisted for months before anyone looks.
Auditors increasingly expect continuous or near-continuous analysis rather than point-in-time snapshots. When your evidence is a spreadsheet timestamped three months before the audit period, it raises questions about what happened in between. SAP Community's overview of cross-system SoD risk reinforces the need for continuous monitoring across interconnected applications.
What Does a Practical SoD Ruleset Look Like?
A ruleset defines the combinations of SAP authorisations that should not coexist within a single user or role. Each rule maps a pair of business functions to the transaction codes and authorisation objects that enable them.
For mid-market teams, starting with a targeted set of high-impact rules produces better results than deploying a ruleset with thousands of combinations. Focus initially on conflicts involving financial postings, vendor and customer master data maintenance, payment processing and user administration.
Your ruleset should be documented, versioned and approved by a defined owner. Auditors want to see that the same rule logic applied consistently across reporting periods, not a ruleset assembled from scratch each time an audit begins.
How Do You Identify Your Highest-Priority SoD Risks?
Not every SoD conflict carries the same weight. A conflict involving purchase order creation and goods receipt approval poses a direct financial control risk. A conflict between low-sensitivity reporting transactions may warrant monitoring but not immediate remediation.
Step 1: Map critical business processes to SAP transaction codes. Focus on procure-to-pay, order-to-cash and financial closing, where control failures carry the greatest financial impact.
Step 2: Run a baseline SoD analysis. Generate a current conflict report across all active users and rank results by severity.
Step 3: Assess actual usage of conflicting authorisations. A user who holds a conflict but has never executed one of the relevant transactions presents a lower immediate risk.
Step 4: Classify each finding as remediate, mitigate or accept. Remediation removes the conflict. Mitigation applies a compensating control an auditor can verify. Acceptance documents a business justification.
Who Should Own SoD Review in a Lean Team?
In larger enterprises, dedicated GRC teams manage SoD governance. Mid-market organisations rarely operate with that structure. The most effective approach assigns ownership to the business process owner for each critical area rather than concentrating all responsibility within IT or the security administration function.
The finance manager owns procure-to-pay and financial posting conflicts. The sales operations lead owns order-to-cash conflicts. HR owns payroll and personnel administration conflicts. Each owner reviews the conflicts in their area, decides on remediation or mitigation, and signs off on any accepted risks.
This structure produces two outcomes auditors value. First, it demonstrates that the people closest to the business process are making access decisions. Second, it distributes the review workload so that no single person is rubber-stamping thousands of line items without context.
How Do You Run a User Access Review That Produces Real Evidence?
Traditional access review campaigns ask managers to certify every authorisation for every user in their team. The outcome is predictable: reviewers face a list of technical role names, approve everything to meet the deadline, and the exercise produces a compliance record with minimal actual scrutiny.
A more effective approach focuses on what changed. Delta-based reviews present only the authorisations added or modified since the previous review cycle. This reduces the volume of decisions, keeps reviewers focused on the access that actually needs attention, and produces a more credible evidence trail.
Present access in business language, not technical role names. A reviewer should see "can create vendor master records" rather than a role identifier. When the risky items are flagged and prioritised, the reviewer spends their time on the decisions that matter.
What Evidence Should You Maintain Between Audits?
Auditors expect a control record that demonstrates continuous governance, not a set of documents assembled during the audit preparation window. The strongest evidence packages include:
Step 5: Maintain a current, versioned SoD ruleset with documented approval. This proves your conflict definitions are deliberate and consistent.
Step 6: Retain timestamped conflict reports at regular intervals. Monthly or quarterly outputs demonstrate that your team monitors access risk on a defined cadence.
Step 7: Archive review decisions with the reviewer identity, date and rationale. Every decision should be traceable to a named individual. Spreadsheet-based approaches typically fail here.
Step 8: Document compensating controls with evidence of execution. Retain evidence that mitigating controls were actually performed, not just that a process document exists.
How Can Mid-Market Teams Build a Repeatable Audit Preparation Process?
Audit readiness is not a project with a start and end date. It is a set of recurring activities that keep your access risk position current. For mid-market teams, the priority is building a cadence that is sustainable with the resources available.
Run SoD analysis on a monthly cadence at minimum. Schedule user access reviews quarterly, using delta-based reviews to keep the scope manageable. Review and update your ruleset annually or after significant changes to your SAP landscape, such as a module implementation or migration.
Assign a single coordinator, typically the SAP security administrator or compliance manager, who tracks review completion, chases outstanding decisions and ensures that evidence is stored consistently. This role does not own the risks, but it ensures the process runs on schedule.
In Summary: Where to Start with SAP Audit Readiness
Building a clearer SAP access risk process before the next audit starts with four fundamentals: a documented SoD ruleset, a prioritised conflict analysis, named ownership for each risk area, and an evidence discipline that runs continuously rather than on demand.
Mid-market teams do not need the same tooling or headcount as large enterprises to achieve this. A structured approach, clear accountability and the discipline to maintain evidence between audits will consistently produce stronger outcomes than reconstructing documentation under pressure.
CERPASS supports this approach with SAP BTP-based SoD analysis, user access reviews, access monitoring and customisable dashboards designed for teams that need audit-ready evidence without a lengthy implementation. Request a consultation to discuss how your team can build a sustainable access risk process.
FAQs About SAP Audit Readiness for Mid-Market Teams
What is the most common SoD conflict auditors flag in SAP?
One of the most frequently flagged conflicts involves a user who can both create a vendor master record and release a payment. This combination allows a single person to set up a fictitious vendor and direct funds to it. Auditors focus on procure-to-pay conflicts because the financial exposure is direct and measurable.
How often should mid-market teams run SoD analysis?
Monthly analysis is a practical cadence for most mid-market organisations. This frequency catches conflicts introduced by role changes or new user provisioning before they persist across an entire audit period. CERPASS automates this analysis against your live SAP landscape through its deployment approach, so running it monthly requires minimal manual effort.
Can you achieve audit readiness without a dedicated GRC team?
Yes. Mid-market teams achieve audit readiness by distributing SoD review ownership to business process owners rather than centralising it within a GRC function. The finance manager reviews financial posting conflicts, sales reviews order-to-cash conflicts, and a coordinator ensures the process stays on schedule.
What evidence do auditors expect from SAP access reviews?
Auditors expect a documented ruleset, timestamped conflict reports, review decisions traced to named individuals, and evidence that compensating controls were actually executed. CERPASS stores this evidence automatically, so your team can produce the required documentation without assembling it from multiple sources before each audit.
How does CERPASS help mid-market teams with SAP audit readiness?
CERPASS provides SAP BTP-based SoD analysis, user access review campaigns, access monitoring and customisable dashboards. It presents access in business language so reviewers understand what they are certifying, flags high-risk items for priority attention, and maintains an audit-ready evidence trail throughout the year.